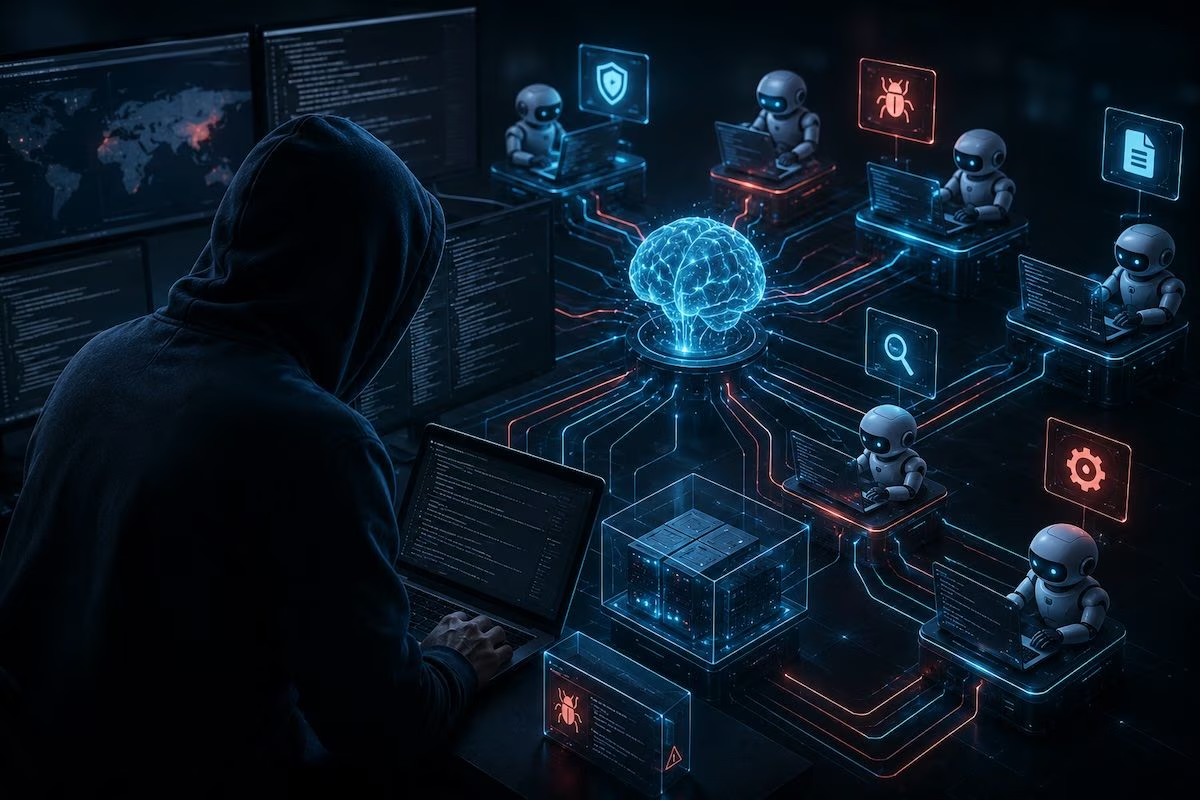
Artificial intelligence is not only changing the way texts are written or programs developed, but it can also speed up the preparation of tools used in cyber attacks. Some hackers have already started using multiple agents based on this technology within real digital “assembly lines”, in which different activities are distributed and carried out in parallel.
Such systems can reduce development and testing phases that previously would have required weeks and numerous manual attempts to just a few days, without eliminating human control.
AI agents have accelerated the development of attack tools
This change is concretely demonstrated by a case identified in May 2026 within an organization’s compromised network. Analysts discovered an unauthorized device that hosted a platform intended for the creation and testing of programs to be used in the post-intrusion phases. The episode is described in the Sophos AI Security 2026 Report and concerns a subject identified with the acronym STAC6994.
To verify its effectiveness, the infrastructure included several virtual machines, i.e. computers simulated using software. Some had different EDR systems installed, tools that monitor devices to detect suspicious behavior. The results were then compared with those obtained in an unprotected environment, used as a reference. In this way it was possible to understand which executables were blocked, modify them and test them again before possible use.
The system was made up of around 12 AI agents, who helped produce nearly 80 modules and experiment with over 70 evasion techniques, i.e. methods designed to prevent the code from being detected by security software. Each had a specific task: one coordinated the main activities and defined the rules, while the others were responsible, among other things, for preparing the virtual environments, documenting the results, subjecting the modules to checks and analyzing errors.
What artificial intelligence actually did
The process was divided into several phases. The agents consulted technical articles, extracted the offensive procedures described, identified the resources necessary to reproduce them and set up the laboratory. After each run, they looked at what worked and what was caught, then tweaked the code or configuration to start a new attempt.
At the heart of the architecture was a modular generator written in Python. The program applied different levels of encryption and measures designed to hinder their recognition to the payloads, i.e. the components intended to carry out the malicious actions. It then produced customized executables in the Rust and Go languages. The result was not a single malware, but a set of parts that could be combined and quickly modified.
The main advantage came from the possibility of performing numerous attempts in parallel. A programmer would have to review the technical sources, set up the laboratory, compile the software, start each test, examine the outcome and manually correct the errors. Instead, the agents could distribute the tasks among themselves and repeat the cycle many more times in the same amount of time.
The 12 models did not act alone and were not integrated into the malware
The level of automation should not be confused with a fully autonomous attack. From the data collected, it emerges that the process used to circumvent EDRs still involved checks and corrections by operators. AI handled part of the workflow and speeded up verification, but was not incorporated into the programs distributed to victims.
Even the results declared by the agents themselves must be read with caution. The documentation produced during the tests reported almost universal success against the protection systems, but the analysts specified that the available evidence did not fully confirm this conclusion. The most significant fact is therefore not the existence of software capable of overcoming any defense, but the speed with which numerous variants could be created and evaluated.
Furthermore, the tools developed were not confined to one experiment. The operator linked to STAC6994 was subsequently associated with ransomware distribution and data theft, indicating the system’s use in concrete operations.
Why AI can make cyberattacks harder to stop
The novelty does not necessarily consist in the appearance of techniques never seen before. Above all, AI can multiply the number of tests and shorten the time needed to adapt the software to the defenses encountered. When a variant is detected, you can analyze the reason for the block, change it, and quickly repeat the cycle.
The same principle can be applied to other criminal activities. Generative systems allow, for example, to prepare more convincing phishing messages in different languages, or to create images, profiles and synthetic voices for social engineering fraud. The report also highlights the clandestine sale of access keys to AI services and the spread of fake programs that imitate legitimate tools to install malicious software.
However, attacks orchestrated almost entirely by artificial intelligence remain rare and do not yet represent the prevailing scenario. Initial access to a network, movements between systems, and theft of information can also leave traces that security solutions can detect.