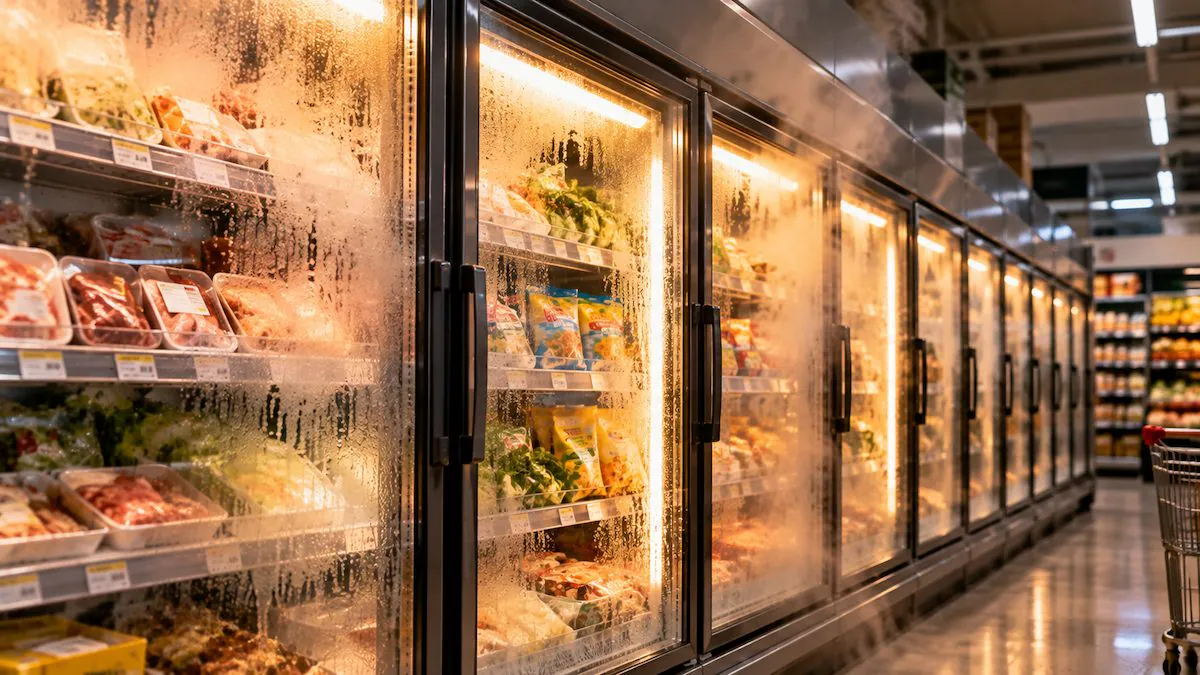
In France, an unusual hacker attack involved large-scale retail trade: the refrigerators in hundreds of supermarkets began to heat up, reaching temperatures between 50°C and 80°C. The high temperatures have compromised the conservation of large quantities of fresh and frozen products, forcing shops to throw away the goods and causing millions of euros in damage.
The problem was not caused by a spontaneous failure, but by a hacker attack against the computer systems that control the refrigeration systems, carried out on the night between 11 and 12 October. The attackers were in fact able to remotely alter the defrost cycles.
What happened in French supermarkets during the hacker attack
According to initial reconstructions, the attack affected around 300 stores of the Les Mousquetaires group, which includes the Intermarché and Netto brands, as well as 80 Carrefour supermarkets and the same number of the Coopérative U network. Some E.Leclerc and Monoprix stores were also hit. The overall budget remains provisional.
The effects of the attack emerged especially in the early hours of the morning, when the staff of several supermarkets found the products stored in the refrigerated counters and in the cold rooms which were now unusable. In Gradignan, near Bordeaux, a delivery worker discovered the anomaly when he found the warehouse of a store flooded. Fires and damage to equipment were also reported and investigations are underway.
In several stores, overheating has caused the interruption of the cold chain, which is essential for properly preserving food. When these remain for hours at too high temperatures, cooling them again is not enough to guarantee their safety, also because during defrosting the bacteria can multiply again. To avoid risks to the health of consumers, the stores concerned therefore had to eliminate the damaged goods. According to initial estimates, losses could reach several tens of millions of euros at a national level, although a definitive quantification is not yet available.
The Paris Prosecutor’s Office has opened an investigation, while the French government has asked ANSSI, the national agency for cybersecurity, to investigate the matter further. Contacts were also initiated with the authorities of other European countries to verify whether other plants were also exposed.
How they sent them haywire by activating defrost at 50°C
In supermarkets, refrigerated counters and cold rooms can be connected to electronic control units that allow you to regulate temperatures, report any anomalies and program operations such as defrosting. Technicians can manage multiple systems through a single interface and even intervene remotely, when the system allows it. A useful possibility for maintenance, which however can represent a security risk if the Internet connection is not adequately protected, as can also happen with connected household appliances.
In the French case, refrigeration management devices produced by the Danish company Danfoss were compromised. Hackers were thus able to change the settings of multiple devices without physically intervening in the stores.
To cause overheating, a completely normal function of refrigerators, automatic defrost, was exploited. During cooling, ice can form on the evaporator, i.e. the component that removes heat from the internal environment. When it accumulates, this hinders heat exchange and reduces the efficiency of the system. To eliminate it, defrost cycles are periodically carried out, a procedure also present in many domestic refrigerators.
During this operation, cooling is temporarily interrupted and, depending on the system, the ice can be melted using electrical resistors or hot gas coming from the refrigeration circuit. Once the cycle is finished, the temperature gradually returns to the expected values. However, if defrosting takes too long, food can deteriorate and even equipment risks being damaged.
This is exactly what happened in French supermarkets. The attackers set the defrost temperature at 50°C, extending the duration of the operation from one to eight hours. The change delayed the activation of the alarms and therefore the intervention of the staff. In a store in La Haye, Normandy, temperatures of up to 80°C were reached, causing some furniture components to melt.
However, it is not yet clear how the hackers initially managed to access the devices. On 12 October, CERT-FR, the French cyber incident response centre, confirmed numerous compromises of Danfoss AK-SM and AK-SC series control units, recommending limiting or interrupting access to management interfaces exposed on the Internet.
Some vulnerabilities of these devices were already known. This summer, security researchers at Claroty published a study on the Danfoss AK-SM 800A model, describing flaws that could allow it to bypass authentication and execute commands remotely. The manufacturer had already distributed the corrective updates, but it was not proven that these specific weaknesses were exploited in the French attack.
Danfoss also explained that a large part of the affected units were made up of obsolete products, which no longer receive security updates. A refrigerator can therefore continue to cool correctly even if the firmware of the control unit that manages it, i.e. the software integrated into the device, has vulnerabilities. To reduce these risks, it is important to install available fixes, replace devices that are no longer supported, and limit remote access to authorized individuals only.
The precedents
By the end of August 2026, some supermarkets on US military bases had already reported similar malfunctions with their refrigeration systems. In several stores, refrigerators and freezers had gone into defrost mode, causing numerous foods to spoil. At least six facilities had confirmed the problems and the military authorities opened investigations, also involving departments specialized in cybercrime.
In that case, however, it was not established that the failures were caused by a hacker attack, nor was there a connection with what happened subsequently in France.
However, there are documented precedents of cyber attacks against the control systems of other infrastructures. In November 2023, for example, cybercriminals compromised PLCs (programmable logic controller), programmable electronic devices also used in US water systems to automate certain operations. According to CISA, the US agency for information and infrastructure security, the attackers had exploited the presence of controllers accessible via the Internet and protected by default passwords (such as 1111) or even none at all, managing to modify their configurations and hinder access by operators.